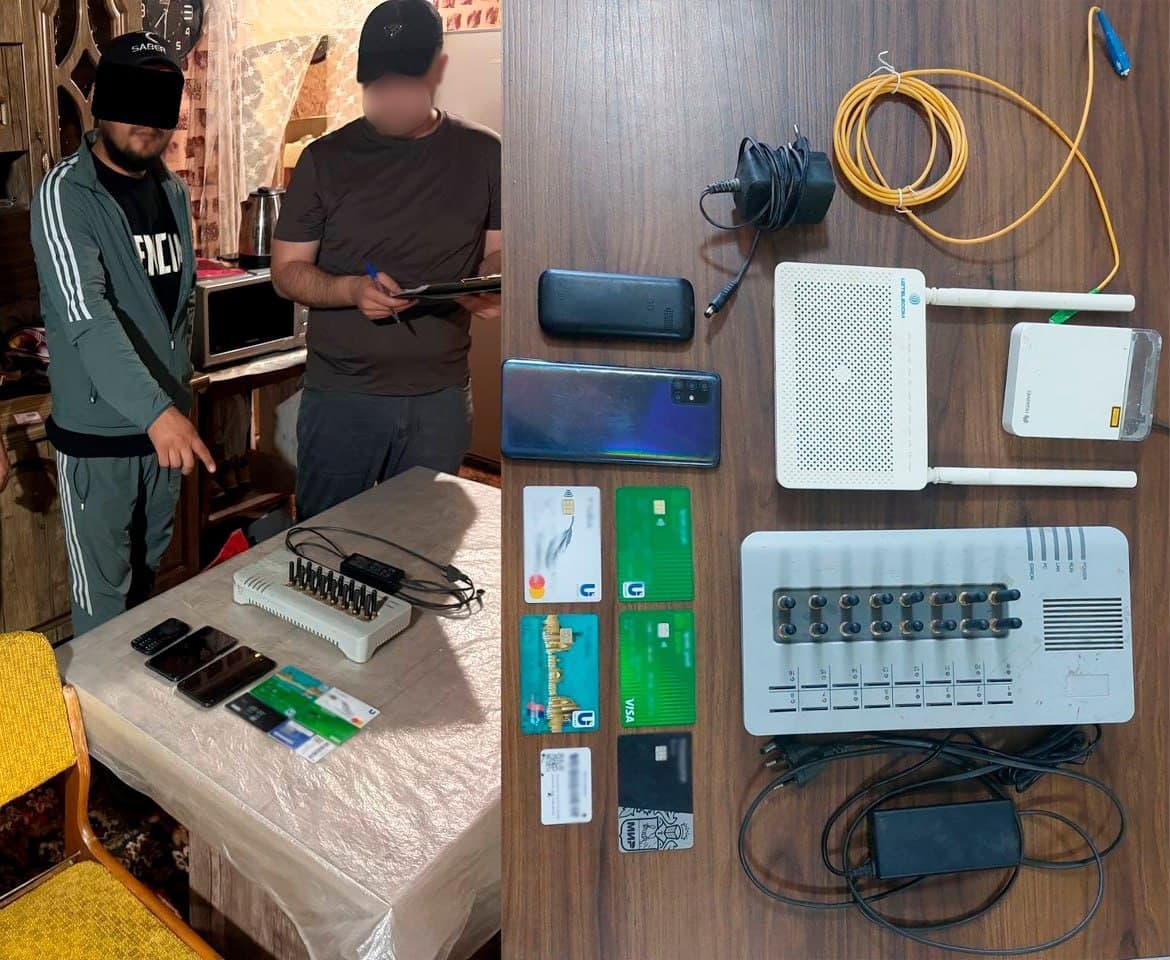
Reportedly, the group members, who are citizens of various countries, used malicious software to steal money from people's bank cards by gaining access to their personal data.
The perpetrators operated through a dedicated Telegram group, where they sent APK files to users. These files contained viruses that infected the victims’ phones. As a result, the attackers gained access to sensitive information such as SMS codes, contacts, call histories, and banking details.
Through these illegal means, the group managed to embezzle nearly 1 billion UZS from the bank cards of 177 individuals via unauthorized transactions. All operations were monitored and coordinated through a call center.
Investigations are currently ongoing to identify other members of the criminal group and to fully uncover the extent of the crime. A criminal case has been initiated under relevant articles of the Criminal Code, and the suspects have been detained in accordance with procedural law.